Buy playerstore.eu ?
We are moving the project
playerstore.eu .
Are you interested in purchasing the domain
playerstore.eu ?
domain@kv-gmbh.de · 0541-91531010
Buy playerstore.eu ?
Does the B450 Gaming Plus Max have TPM?
The B450 Gaming Plus Max does not have a built-in TPM (Trusted Platform Module) chip. However, you can add a TPM module to the motherboard if you need to use TPM for security features such as BitLocker encryption. Keep in mind that not all motherboards come with a TPM header, so you may need to check the specifications of the B450 Gaming Plus Max to ensure compatibility with a TPM module. **
"Does my Asus B450-F Gaming support TPM 2.0?"
Yes, the Asus B450-F Gaming motherboard does support TPM 2.0. This motherboard has a TPM header, which allows you to connect a TPM module to enable TPM functionality. TPM (Trusted Platform Module) is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption and secure boot. By adding a TPM module to the motherboard, you can enhance the security of your system and protect sensitive data. **


Similar search terms for Tpm
Top-Angebote
Products related to Tpm:
-
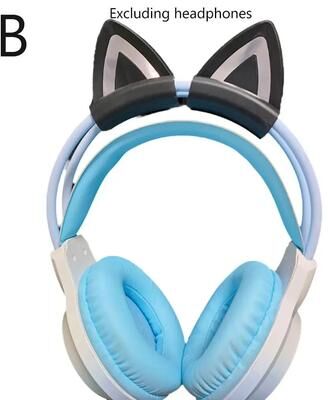
Inspire Essentials CuteCat Headphone Accessories Cat Ear Attachments For Gaming Headsets blackAdd a playful touch to your setup and stand out instantly. These cat ear headphone accessories are designed to transform your ordinary headset into something fun and expressive. Made from soft silicone, they are lightweight, comfortable, and easy to...34,98 $*Shipping: 0,00 $Secure redirect to the provider
-
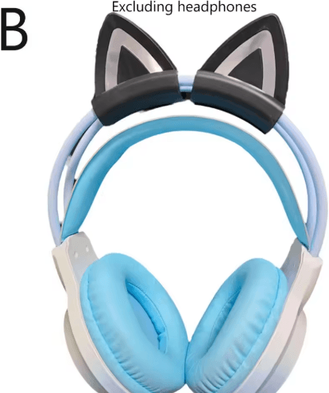
Inspire Picks Cute Silicone Cat Ear Accessories For Gaming Headsets blackAdd playful style to your favorite headphones with these adorable Cat ear headset accessories designed for gamers, streamers, and music lovers. Made from lightweight silicone material, these decorative attachments easily clip onto compatible...34,93 $*Shipping: 0,00 $Secure redirect to the provider


-
What is BitLocker TPM?
BitLocker TPM (Trusted Platform Module) is a security feature in Windows operating systems that uses a hardware component called TPM to provide enhanced protection for data stored on a computer's hard drive. TPM is a microchip that securely stores encryption keys, passwords, and other sensitive information to help protect against unauthorized access to the system. When BitLocker TPM is enabled, the encryption keys are securely stored in the TPM, making it more difficult for attackers to access the data even if they physically remove the hard drive from the computer. **
-
Can't you activate TPM?
Yes, TPM (Trusted Platform Module) can be activated on compatible devices through the device's BIOS settings. However, not all devices have TPM built-in, so it's important to check the device's specifications to see if TPM is available. Once activated, TPM provides hardware-based security features such as secure boot, device encryption, and key management to help protect sensitive data and ensure the integrity of the system. **
-
What exactly is TPM 2.0?
TPM 2.0, which stands for Trusted Platform Module 2.0, is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption, authentication, and key management. It is a microcontroller that is typically integrated into computer systems to enhance security by securely storing sensitive information, such as encryption keys, digital certificates, and passwords. TPM 2.0 helps protect against various security threats, including unauthorized access, malware attacks, and data breaches, by providing a secure environment for sensitive data and cryptographic operations. **
-
How do I activate TPM?
To activate TPM (Trusted Platform Module) on your computer, you will need to access the BIOS or UEFI settings. Restart your computer and enter the BIOS/UEFI by pressing a specific key (usually F2, F10, or Del) during the boot-up process. Look for the TPM settings in the security or advanced settings section and enable TPM. Save the changes and exit the BIOS/UEFI settings. TPM should now be activated on your computer. **

How can I update TPM?
To update TPM (Trusted Platform Module), you can follow these steps: 1. Check for TPM firmware updates on the manufacturer's website or through the device's management software. 2. Download the latest TPM firmware update and follow the instructions provided by the manufacturer for installation. 3. Ensure that your device is connected to a stable power source and that all other applications are closed during the update process. 4. Restart your device after the update is complete to ensure that the changes take effect. It's important to regularly check for TPM updates to ensure that your device has the latest security features and bug fixes. **
How can one delete TPM?
To delete TPM (Trusted Platform Module) on a computer, you would need to access the computer's BIOS or UEFI settings. Once in the settings, you can navigate to the security or TPM section and find the option to clear or reset the TPM. This will remove any existing TPM data and settings from the computer. It's important to note that deleting TPM may have implications for the computer's security and functionality, so it should only be done if necessary and with caution. **
Top-Angebote
Products related to Tpm:
-
Asus TPM-SPI V2.0 Security TPM ModuleThe ASUS TPM SPI V2.0 Security Module is designed to enhance computer security by providing dedicated hardware based protection for compatible systems. It helps securely store encryption keys, digital certificates, passwords and other sensitive information. Using a 14-1 pin SPI interface, the module is designed for compatible ASUS motherboards and systems that support the TPM SPI standard. It provides a dedicated Trusted Platform Module solution for systems requiring hardware based security features. The module uses the Nuvoton NPCT750 security chip and complies with the Trusted Computing Group TPM 2.0 specification. This allows it to support security functions that help protect platform integrity and digital identities. Security certifications include Common Criteria EAL4+ and FIPS 140-2. The module also meets CE and RoHS compliance requirements, providing a certified solution for compatible computing platforms. The ASUS TPM SPI V2.0 is a compact internal security accessory designed for straightforward motherboard integration. Before installation, compatibility should be checked carefully because TPM SPI and TPM LPC modules use different pin definitions and are not interchangeable.15,99 £*Shipping: 0,00 £Secure redirect to the provider
-
Inspire Picks Cute Silicone Cat Ear Accessories For Gaming Headsets whiteAdd playful style to your favorite headphones with these adorable Cat ear headset accessories designed for gamers, streamers, and music lovers. Made from lightweight silicone material, these decorative attachments easily clip onto compatible...34,93 $*Shipping: 0,00 $Secure redirect to the provider
-
Inspire Essentials CuteCat Headphone Accessories Cat Ear Attachments For Gaming Headsets blackAdd a playful touch to your setup and stand out instantly. These cat ear headphone accessories are designed to transform your ordinary headset into something fun and expressive. Made from soft silicone, they are lightweight, comfortable, and easy to...34,98 $*Shipping: 0,00 $Secure redirect to the provider
-
Does the B450 Gaming Plus Max have TPM?
The B450 Gaming Plus Max does not have a built-in TPM (Trusted Platform Module) chip. However, you can add a TPM module to the motherboard if you need to use TPM for security features such as BitLocker encryption. Keep in mind that not all motherboards come with a TPM header, so you may need to check the specifications of the B450 Gaming Plus Max to ensure compatibility with a TPM module. **
-
"Does my Asus B450-F Gaming support TPM 2.0?"
Yes, the Asus B450-F Gaming motherboard does support TPM 2.0. This motherboard has a TPM header, which allows you to connect a TPM module to enable TPM functionality. TPM (Trusted Platform Module) is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption and secure boot. By adding a TPM module to the motherboard, you can enhance the security of your system and protect sensitive data. **
-
What is BitLocker TPM?
BitLocker TPM (Trusted Platform Module) is a security feature in Windows operating systems that uses a hardware component called TPM to provide enhanced protection for data stored on a computer's hard drive. TPM is a microchip that securely stores encryption keys, passwords, and other sensitive information to help protect against unauthorized access to the system. When BitLocker TPM is enabled, the encryption keys are securely stored in the TPM, making it more difficult for attackers to access the data even if they physically remove the hard drive from the computer. **
-
Can't you activate TPM?
Yes, TPM (Trusted Platform Module) can be activated on compatible devices through the device's BIOS settings. However, not all devices have TPM built-in, so it's important to check the device's specifications to see if TPM is available. Once activated, TPM provides hardware-based security features such as secure boot, device encryption, and key management to help protect sensitive data and ensure the integrity of the system. **
Similar search terms for Tpm
-
Inspire Picks Cute Silicone Cat Ear Accessories For Gaming Headsets blackAdd playful style to your favorite headphones with these adorable Cat ear headset accessories designed for gamers, streamers, and music lovers. Made from lightweight silicone material, these decorative attachments easily clip onto compatible...34,93 $*Shipping: 0,00 $Secure redirect to the provider
-
Inspire Picks Cute Silicone Cat Ear Accessories For Gaming Headsets whiteAdd playful style to your favorite headphones with these adorable Cat ear headset accessories designed for gamers, streamers, and music lovers. Made from lightweight silicone material, these decorative attachments easily clip onto compatible...34,93 $*Shipping: 0,00 $Secure redirect to the provider
-
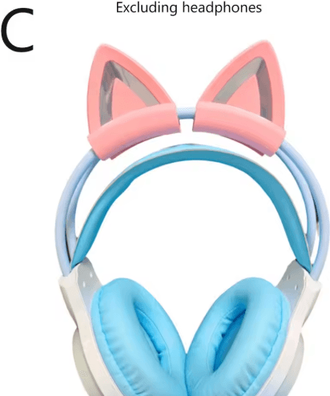
Inspire Picks Cute Silicone Cat Ear Accessories For Gaming Headsets pinkAdd playful style to your favorite headphones with these adorable Cat ear headset accessories designed for gamers, streamers, and music lovers. Made from lightweight silicone material, these decorative attachments easily clip onto compatible...34,93 $*Shipping: 0,00 $Secure redirect to the provider
-
What exactly is TPM 2.0?
TPM 2.0, which stands for Trusted Platform Module 2.0, is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption, authentication, and key management. It is a microcontroller that is typically integrated into computer systems to enhance security by securely storing sensitive information, such as encryption keys, digital certificates, and passwords. TPM 2.0 helps protect against various security threats, including unauthorized access, malware attacks, and data breaches, by providing a secure environment for sensitive data and cryptographic operations. **
-
How do I activate TPM?
To activate TPM (Trusted Platform Module) on your computer, you will need to access the BIOS or UEFI settings. Restart your computer and enter the BIOS/UEFI by pressing a specific key (usually F2, F10, or Del) during the boot-up process. Look for the TPM settings in the security or advanced settings section and enable TPM. Save the changes and exit the BIOS/UEFI settings. TPM should now be activated on your computer. **
-
How can I update TPM?
To update TPM (Trusted Platform Module), you can follow these steps: 1. Check for TPM firmware updates on the manufacturer's website or through the device's management software. 2. Download the latest TPM firmware update and follow the instructions provided by the manufacturer for installation. 3. Ensure that your device is connected to a stable power source and that all other applications are closed during the update process. 4. Restart your device after the update is complete to ensure that the changes take effect. It's important to regularly check for TPM updates to ensure that your device has the latest security features and bug fixes. **
-
How can one delete TPM?
To delete TPM (Trusted Platform Module) on a computer, you would need to access the computer's BIOS or UEFI settings. Once in the settings, you can navigate to the security or TPM section and find the option to clear or reset the TPM. This will remove any existing TPM data and settings from the computer. It's important to note that deleting TPM may have implications for the computer's security and functionality, so it should only be done if necessary and with caution. **
* All prices are inclusive of VAT and, if applicable, plus shipping costs. The offer information is based on the details provided by the respective shop and is updated through automated processes. Real-time updates do not occur, so deviations can occur in individual cases. ** Note: Parts of this content were created by AI.